
As a founder, you like to think you’ve hired the cream of the crop. The folks who are experts in their craft, who consistently pull out all the stops, who have the most innovative ideas.
They’ve got to be the same people who stay up to date on the latest and greatest security scams, right? Right?
Even the most talented behind-the-scenes security buffs can put your company’s security at risk. Not because they’re not paying attention, but because threats are constantly changing. Particularly as AI gets better and better.
And your customers are going to want evidence that your employees know their stuff. That evidence is going to come in the form of an audit. And that audit is going to require security awareness training.
Even for a startup dream team, figuring out how to create, deploy, and track security awareness training on top of the million other things on their plates is a tall order. So we’ve broken it down for you.
Below, you’ll find seven strategies to roll out security awareness training that checks all the boxes and gets your great people back to doing what they do best. But first, do you even need security awareness training?
Yes, startups do need security awareness training
Every company needs security awareness training, big or small. Malicious actors are everywhere, and they’re always finding new ways to exploit people.
Your team members may be as sharp as tacks, but sharp people:
- Still open a fake ‘Docusine’ email when they’re tired or get excited about an invite to speak at a fake conference.
- Have a really hard time distinguishing AI-generated voices from real ones (only 60% of the time, according to a 2025 study out of UC Berkeley).
- Could be totally new to the team and not have a sense of what their coworkers sound like over text yet (Oh, they don’t use a bunch of emojis? Or speak with extreme urgency?).
- Use non-approved tools to get work done faster.
As one Redditor puts it: “Users are your main point of vulnerability. Every major security incident we have had in the past 3 years has had a user as the entry point for the attacker so security awareness training is one way to try and reduce that happening.”
Beyond teaching your team best practices, security awareness training is a requirement for most security frameworks. If you ever see your startup selling to an enterprise company, you’ll need to abide by those frameworks.
According to a (little bit jaded) self-identified MSSP manager, the reason to pay for security awareness training is to assure someone you’ve done your due diligence to protect the company.
“Depending on the business context, that ‘someone’ in question can be an auditor, potential court discovery, governmental agencies, your board, or an important stakeholder.”
These VIPs do not mess around when it comes to compliance. Some enterprise prospects will even knock you out of the running outright if they find out you don’t have a SOC 2 report. And while SOC 2 technically has no training requirement, you do need to:
- Attract, develop, and retain people competent to carry out their security responsibilities. They have to know what those are and how to uphold them.
- Hold people accountable for those responsibilities. They have to know the consequences of not sticking to your security rules.
- “Internally communicate information, including objectives and responsibilities for internal control, necessary to support the functioning of internal control.”
Oh, and if you buy cybersecurity liability insurance (a good idea), your provider will likely have a security awareness training mandate, too.
So, yeah, you need training.
7 ways to run security awareness training at a startup without burning out your team
1. Anchor training to onboarding
This might sound obvious, but it’s easy to forget: new employees expect to be drinking from a firehose, learning everything about your company and getting acquainted with the way you do things.
That’s the best time to introduce security awareness training. Folding it into the list of things people just have to get done before they start working in earnest ensures you get that box checked early.
And auditors are looking for it.
SOC 2 auditors, in particular, want to see new hires complete security awareness training in a timely way (between 7 and 30 days) after their start date, depending on your stated policy. Best practice is to have an “access gate” so that users only get access to production systems and customer data after training is marked complete.
2. Stick to short modules
Startup employees are known to “wear many hats.” Sitting through hours and hours of training limits how many of those hats they can wear.
Your goal is to give them the information they need quick enough to slot easily into their workday, but not so quick it goes in one ear and out the other.
The goldilocks length is around ten minutes. Focus on just one kind of threat and make it super relevant to the person watching. For instance, if an employee fails a phishing simulation, trigger a short module right after with a few similar examples to hammer home the lesson while it’s still fresh. Or, if their primary function is finance, tailor the training to attacks that happen to finance teams (especially one that your organization has already experienced).
3. Deliver training in tools people already use
It may not seem like much, but asking your employees to:
- Monitor their inbox for an “Action required: You have 3 pending tasks”-esque email
- Click the link
- Enter their password
- Navigate to the right LMS course
- Take that course
…is a lot, especially when they’re trying to get the next big feature or viral campaign out the door. It’s an even bigger ask if you’re trying to do continuous training, short bursts throughout the year to keep everyone sharp after initial onboarding.
To maximize participation and keep team morale high, you need to deliver training where people already work. For Beth Lopez, CEO of Outfox Health, that was in Slack.
“We spend so much time on Slack, and seeing Herd notifications there allows us to take action right away. I could do the training at any moment to get it done. I didn’t even need my desktop open.”
4. Don’t just rehash the basics
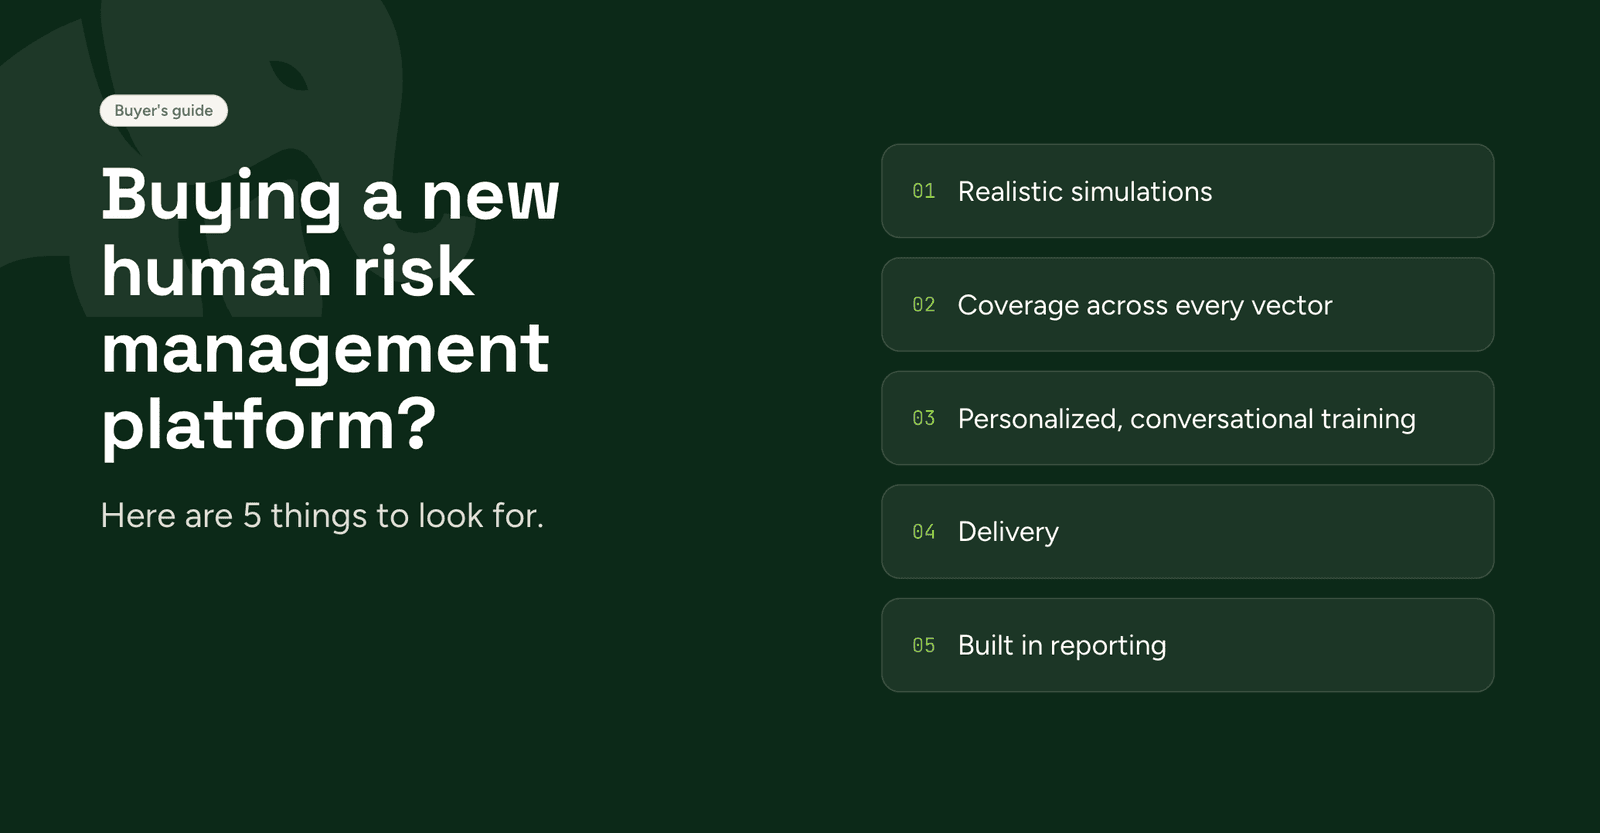
That makes for the most boring training ever, and worse, makes people feel like they can just zone out. Unfortunately, though, most human risk management platforms aren’t built to be entertaining, let alone keep up with the times.
One Redditor shares: “Every program I've seen is just...bad. Like really bad. The kind of thing where you can tell it was made in 2015 and hasn’t been updated since. I need something that works and doesn’t make our devs revolt.”
Now, your trainings don’t have to be as suspenseful as an A24 movie. But when you’re evaluating security awareness training platforms, think about how they present concepts employees might already know about.
Are they showing phishing, password security, ransomware, and social engineering threats in a new light? In a way that makes people go, ‘Oh shoot, I would’ve missed that’?
The best platforms keep people on their toes by:
- Reusing real phishing attempts that employees have previously reported. One Redditor shares: “We started showing people actual phishing emails we’d caught, with names removed. Walking through a real one that hit our inbox lands better than fake examples.”
- Scanning Reddit, security feeds, and X for the most up-to-date scams.
- Learning how your organization works (down to the emojis coworkers use) to make phishing sims hyperrealistic and tailored to each employee’s role at the company.
5. Make training personal
As much as your employees care about the startup they work for, they care more about themselves. So why not frame training as something that benefits them and not just the company?
As a Top 1% Commenter in r/cybersecurity puts it, “One of the things that helps uptake is if you can make it more about the individuals. If the company is breached, payroll may be delayed. Would that be a problem? Sales might miss a target because CRM was down for 2 weeks.
“Also,” they point out, “Learning to spot scams is a way to protect themselves individually. Maybe you don't care if work gets breached, but would you care if you got scammed out of $25k? The lessons apply personally and professionally.”
Concrete, personal stakes beat out abstract compliance. The trick is designing training that makes those stakes feel real.
One way Herd does this is with a voice AI module. Employees record a 10-second voice sample. That gets dropped into an AI duplicator, then gets passed back to them in Slack or Teams alongside the original, and they have to pick which one is fake.
Spoiler: it’s really tough. And it goes to show that the same tech that hackers use to clone a CEO’s voice could just as easily be used to impersonate someone’s mom or trick them into wiring money to a family member in trouble.
6. Timestamp every completion
According to folks in subreddits like r/soc2, even screenshots of training completions get pushback if they don’t clearly show individuals and dates.
What you need is a tool that can automatically log who completed which training and when, and that lets you access that log at any time.
Want to really wow an auditor without creating extra work for yourself? Find a platform that automatically:
- Assigns the right training and simulations to the right people
- Sends them reminders to take trainings assigned to them
- Shows which teams are highest risk
- Shows those teams improving as they undergo more simulations and training over time
7. Right-size your tech
Most security awareness platforms are built for enterprises with a dedicated security team who can manage them. A team very few startups have.
The person likely cobbling together a security awareness program is the CEO, Chief of Staff, or someone else with ops chops. These people rarely have the cyber background, or the time, to tinker with a bunch of different configurations or features.
Beth at Outfox shares, “As CEO, I don’t want to think about security and compliance. I already have thousands of tasks to do a day. Tacking on the load of figuring out which cybersecurity training, policies, and controls we needed to cover was a whole other level I wasn’t prepared for.”
The good news is that there are tools out there that take this weight off your shoulders. And you don’t need a $200,000 GRC analyst to help you.
They’re easy to set up, they’re quick to deploy, and you can even modify them on the fly. Herd, for example, only takes minutes to connect to a ChatOps tool (e.g., Slack or Teams), ingest your security policies, and produce a training module.
Employees get a DM from Herd, start the training, go through the prompts, and Herd automatically timestamps their completion on the backend. Quick and easy.
Check the box, get back to work
The whole point of security awareness training isn’t to turn your employees into part-time security analysts. At a startup, security awareness training needs to do two things: prove your people know enough to keep the company and your customers safe, and give your auditor the evidence for it.
Herd is built to do just that.
With short, engaging modules delivered in Slack or Teams, automatic reminders, timestamps for your auditor, and results you can monitor over time, consider compliance handled. Book a demo to see it in action.